Make good habits familiar.
Rehearse verifying evidence, escalating concerns and involving the right people in a safe, fictional crisis.
Interactive cyber crisis exercises for leadership, security and business teams.
PRACTISE TOGETHER. RESPOND BETTER.
Put your team through a realistic crisis exercise.
With ReFlex, your team makes the calls, sees the consequences and learns together—building the muscle memory for a stronger response.
BEYOND THE SLIDE DECK
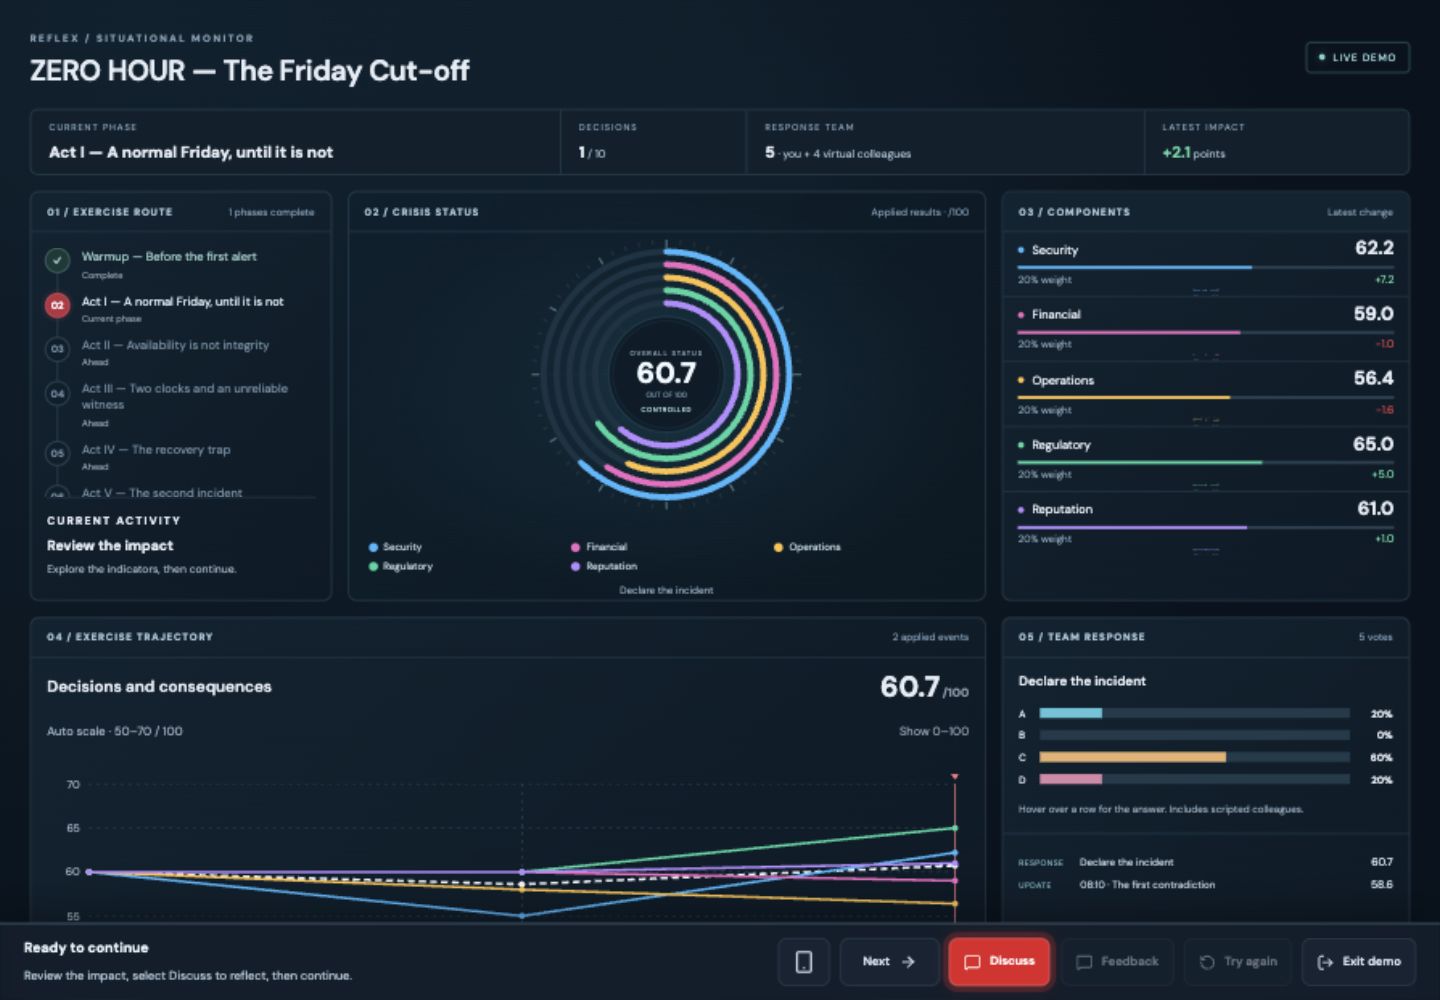
Evolving briefings, participant responses and live indicators keep everyone working from the same situation. Guided reflection turns those decisions into practical actions.
Build cyber fitness and response muscle memory through repeatable, engaging exercises that put cooperation into practice.
CYBER FITNESS THROUGH PRACTICE
Rehearse verifying evidence, escalating concerns and involving the right people in a safe, fictional crisis.
Explore how leadership, security and operations weigh competing priorities. Return to the handoffs that need practice.
Use the decisions and discussion to identify gaps, clarify ownership and agree what to test next.
THE REFLEX EXPERIENCE
A facilitator controls the session. Participants join on their phones or laptops and follow a shared room screen. The dashboard makes the simulated consequences visible.
A CRISIS THAT UNFOLDS
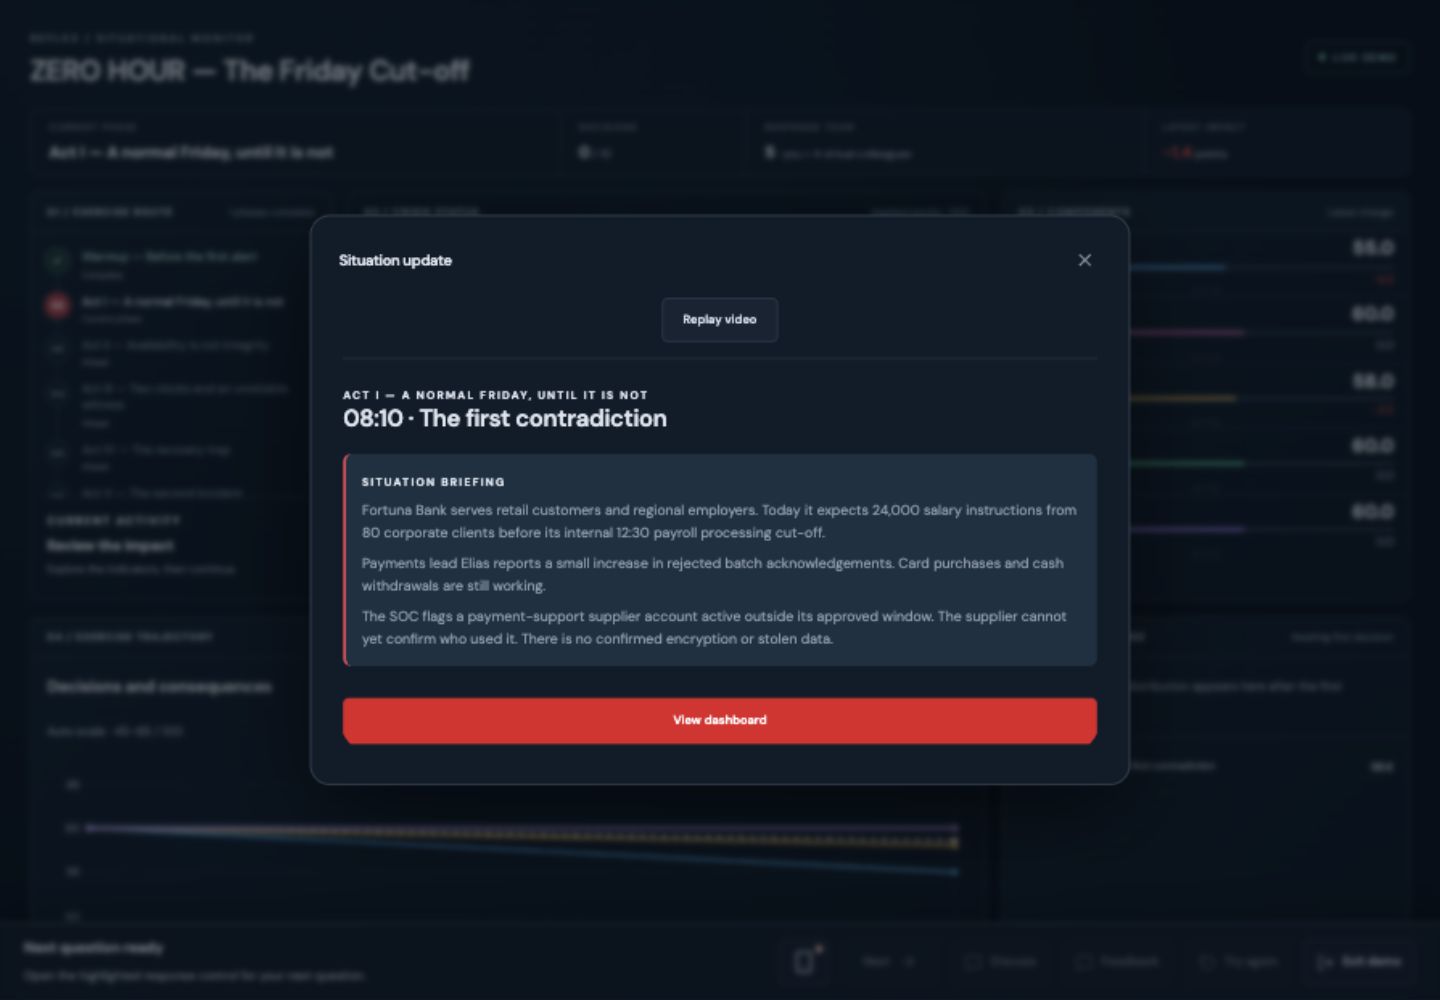
Injects appear above the situation room, keeping the team focused on the information that matters. The live dashboard remains the shared reference throughout the exercise.
EVERY VOICE COUNTS
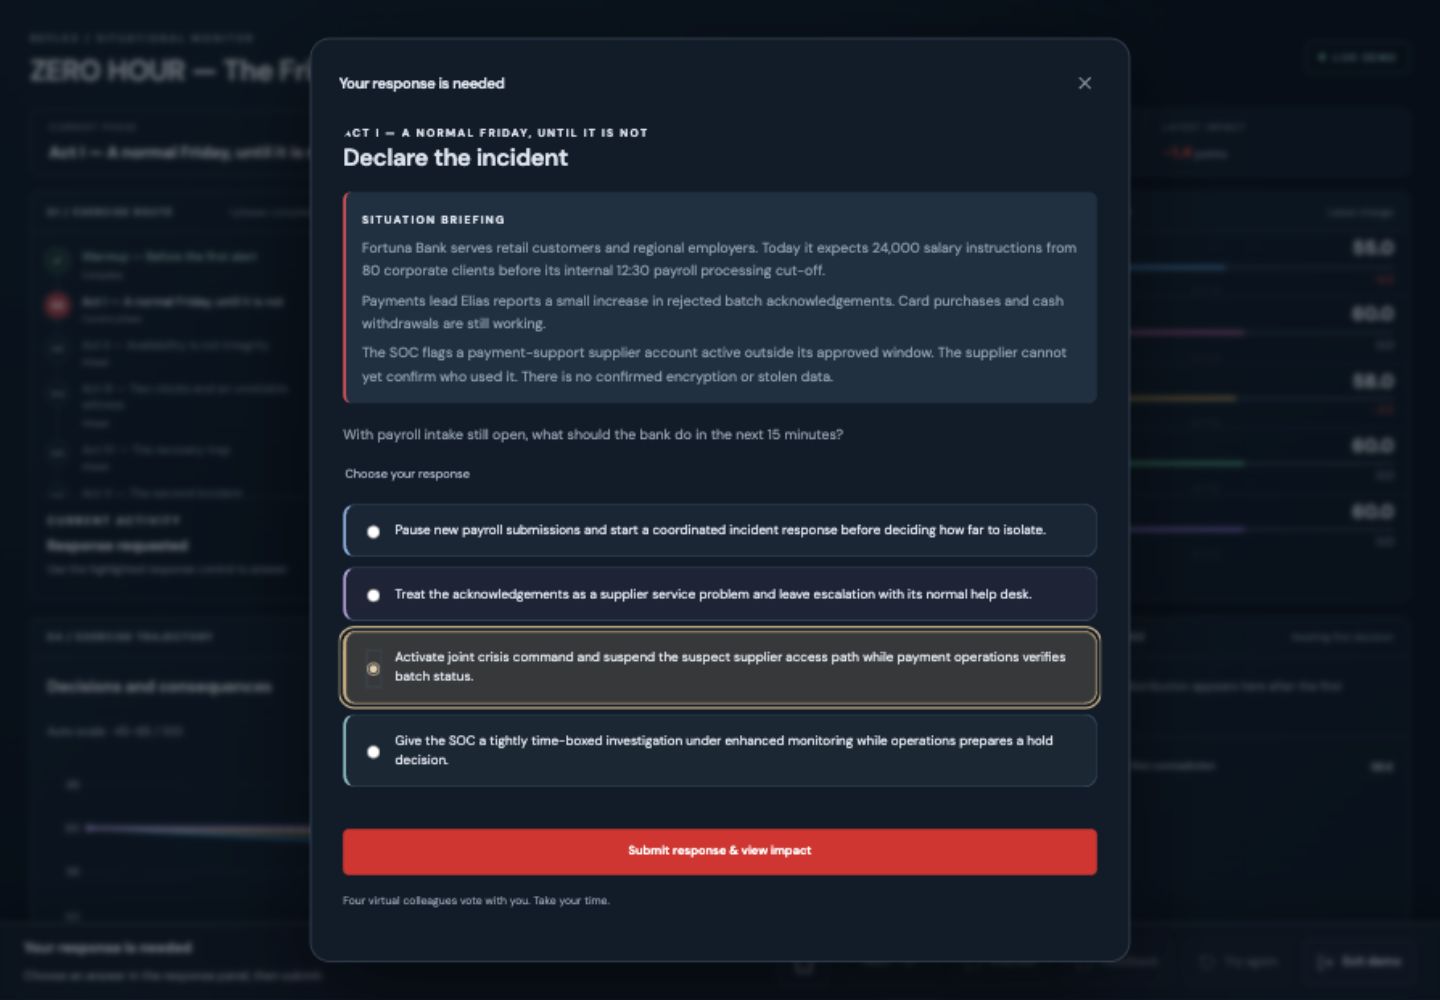
Response choices bring competing priorities into the conversation. Review the combined response, watch its effect and discuss what evidence could change the decision.
In a self-paced demo, four scripted colleagues vote alongside the visitor. A facilitated exercise brings your real team into the discussion.
FACILITATED TEAM EXERCISES
Use the scenario notes and running order to lead a focused session for executives, security teams, operations, communications and other business functions.
EXPLORE BEFORE YOU EXERCISE
Self-paced demos let participants experience the scenario and dashboard before a workshop. Your facilitator shares a separate demo link; the pages here introduce the experience and scenarios.
LOOK INSIDE AN EXERCISE
Explore ZERO HOUR’s story, timeline and training priorities in a detailed scenario overview.
THE SCENARIO PORTFOLIO
Choose a setting that reflects your team’s responsibilities. Each facilitated exercise combines an evolving crisis, shared decisions and discussion. Browse four collections, then search by the story, threat or sector. Group sizes and durations are suggested workshop formats; the facilitator sets the pace.
27 scenarios in four collections
Banking, payment integrity and sensitive financial data.
A fictional Friday cyber crisis at Fortuna Bank. The central question is whether payments and recovery evidence can be trusted, while employers and vulnerable customers cannot wait for perfect information.
At fictional Meridian Bank, a journalist sends a spreadsheet from a public Telegram channel. Some records match customers; several other banks are named. Investigate the source while protecting customers from fraud and communicating what is actually known.
Fictional payment provider RelayPay appears on an extortion site before a busy trading period. Payments still process, but an old migration environment may contain real customer records. Establish the scope, protect service continuity and explain a breach that production availability alone cannot rule out.
Manufacturing, essential networks and the dependencies that keep operations moving.
A fictional cross-sector energy crisis connects an upstream producer, a pipeline operator and a refinery. Practise coordination, supplier access decisions, operational assurance, public communication and recovery across shared dependencies.
At fictional Harborline Logistics, a compromised freight partner account sends altered collection instructions during a busy dispatch window. Loads are delayed, a high-value consignment is disputed and the team must restore trusted release decisions across carriers, warehouses and customers.
A regional electricity distributor loses confidence in part of its remote visibility during a busy evening. A cyber alert overlaps with a localized weather fault. Operators must separate facts from stale telemetry, coordinate field crews and authorize recovery without allowing commercial urgency to override electrical safety.
A fictional European precision-components plant faces a compromised supplier access path, ransomware on enabling IT, unreliable HMI visibility and uncertain control integrity.
Fictional Northline Managed Services faces a compromised shared deployment service during a Friday maintenance window. A multi-day crisis spans customer prioritization, extortion claims, partner access, unreliable restores and an exhausted response team. Each phase adds evidence or a business constraint; leaders must revisit earlier commitments. All times are fictional time jumps.
Westhaven Water faces suspicious maintenance access, conflicting tank readings and a public contamination claim. Coordinate field checks, sustain essential service and decide what can be communicated—and what evidence must authorize recovery.
Aster Reach discovers an unapproved ground-system configuration before a contracted satellite service window. Protect command authority, allocate limited fallback capacity and verify recovery while customers need reliable answers.
A fictional German precision manufacturer confronts a ransomware incident across a compressed three-day story. Teams balance delegated authority, verified production, customer commitments, workforce trust, liquidity and recovery assurance. A functioning machine is not proof that a business can safely deliver.
At fictional Yaochuan Precision Manufacturing in Taiwan, supplier maintenance leaves conflicting traceability records while the production lines remain green. Verify access, reconcile batch evidence and balance safe delivery with customer trust before the logistics cut-off. Mandarin briefings and Traditional Chinese decisions.
A routine support login at Meridian Industrial Services exposes a hidden intrusion across identities, remote administration and recovery infrastructure. The team must act on incomplete evidence, protect a four-hour continuity window and prove that reopening will not restore the attacker’s access.
Fictional Bayline Joint Venture is preparing a mixed-use building for handover. A site tablet shows a changed work package as approved, but the design authority has no matching approval. Keep people and unaffected work safe while establishing which drawings, copies and installed work can be trusted.
Fictional Meridian Connectivity carries business internet and voice services across two regions. An unapproved management change appears while the service overview stays green. Network operations, security and service owners must contain administrative access, preserve evidence and prove which services can safely use a recovered path.
Fictional Lakefield Fresh makes chilled ready-to-eat meals for retailers and direct collection. An ingredient specification and a printed allergen label disagree as the morning dispatch approaches. Food-safety, production, logistics and cyber teams must protect consumers, establish a defensible product boundary and restore only independently accepted production.
Public services, education and care under pressure.
An overnight cyber incident at a shared pathology provider disrupts three hospitals just as the morning schedule begins. Results cannot be assumed current, alternate laboratories have limited capacity, and the network must protect care without improvising clinical procedures.
Fictional Eastmere Council loses access to its citizen portal during a benefits application deadline. The provider confirms a traffic flood, while online claims allege a data leak. Service managers must preserve fair access, coordinate suppliers and recover without losing applications.
At fictional Rowanbridge School, an invitation to try an AI teaching assistant arrives from a familiar contact. A colleague signs in. Before the first bell, their account sends unexpected messages. Protect pupil information, keep learning moving and maintain trust as the facts emerge.
Digital trust, retail operations, supplier access and executive decisions.
A targeted phishing message from a compromised supplier contact installs an implant on a Meridian Research Group workstation. Weeks later, investigators discover foldering: the implant and its operators exchange instructions and responses through unsent mailbox drafts. The incident threatens confidential research and trusted partner access, while ordinary sent-mail searches miss the command channel.
On the morning of a major promotion, a suspicious service-desk account reset precedes disruption to Northstar’s order and warehouse systems. Stores can still serve some customers, but inventory, collection promises and carrier handovers are becoming unreliable. Leaders must decide what to sell, fulfil, refund and reopen.
Aster Services has connected its support assistant to a knowledge base and customer-service tools. Malicious instructions in a supplier document cause it to expose restricted contract information and recommend unauthorized credits. The team must separate model behavior from failed authorization, protect customers and decide which capabilities can safely return.
At fictional Halcyon Group, a disruptive cyber incident stops customer services and payroll preparation. The executive team has limited cash, conflicting recovery estimates and an unverified extortion claim. Leaders must establish authority, protect essential commitments and explain what they know. Technical specialists provide plain-language briefs; no configuration or forensic expertise is required.
A supplier advisory interrupts a customer launch at fictional Lumen Trade Services. An everyday desktop application has delivered an implant to a subset of endpoints. The team must map exposure, protect privileged access and restore trusted workstations while explaining what the evidence does—and does not—show.
At fictional Alder & Vale Advisory, a transaction closes at 12:00. A shared deal room contains a changed signing pack that a client says they never approved. Preserve the matter record, verify instructions and restore a controlled way to work without treating a clean IT system as client consent.
At fictional Cedar Mutual, a broker integration submitted unexpected coverage endorsements overnight. A genuine claim arrives against a disputed record. Contain the integration, reconstruct the authoritative record and sustain fair policyholder service without confusing an IT rollback with a coverage decision.
At fictional Northstar Services, the SOC detects a suspicious process on an internet-facing collaboration server. An external incident-response team joins the customer’s responders. Decide how to authorise useful help, stop active access, build a defensible scope and restore service through evidence-backed gates rather than a promise that every attacker has been found.
Try another search, sector or difficulty.
TRAIN. REPEAT. IMPROVE.
Build response muscle memory through purposeful practice.
Strengthen team habits through reflection and follow-through.